Managing AI Across Subsidiaries: How Holding Companies Eliminate Cross-Company Data Leaks
How multi-entity conglomerates and corporate groups deploy intelligent automation across automotive, healthcare, and retail subsidiaries without risking proprietary cross-contamination.
Managing AI Across Subsidiaries: How Holding Companies Eliminate Cross-Company Data Leaks
For corporate conglomerates, holding companies, and multi-brand groups, adopting artificial intelligence poses a unique operational paradox.
On one hand, corporate leadership wants centralized visibility, shared enterprise licensing discounts, and unified brand standards across all operating companies. On the other hand, subsidiary business units often operate in completely different regulatory regimes—such as an automotive dealership group operating alongside a healthcare diagnostics subsidiary and a financial lending arm.
Under no circumstances can customer financial profiles from Company B appear in automated responses generated for Company A.
The Fatal Flaw in Conventional Business Software
Most commercial conversational tools force holding companies into one of two terrible compromises:
- The Shared Account Risk: Forcing all subsidiaries into a single platform workspace, where a customer service bot for your retail brand accidentally retrieves supplier contracts or VIP customer lists belonging to your luxury automotive division.
- The Fragmented Account Sprawl: Requiring the holding company to procure, configure, and monitor entirely separate billing accounts and software instances for each child company—destroying executive oversight and blowing up annual IT budgets.
The BhavitramAI Multi-Organization Solution
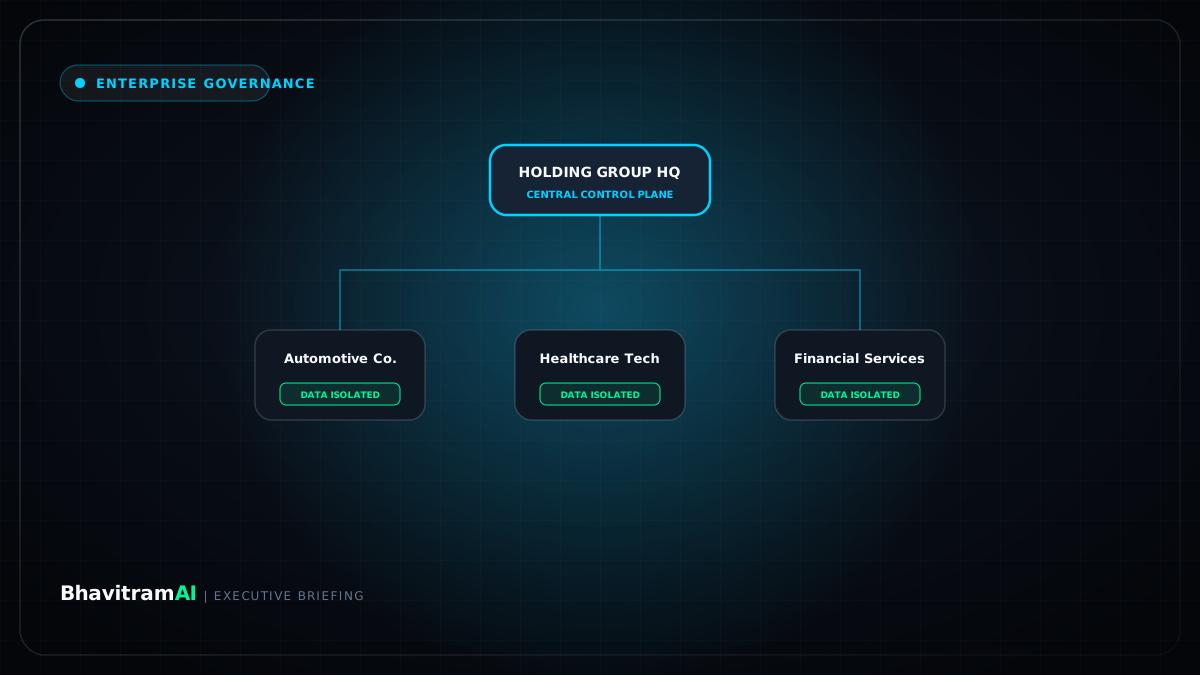
BhavitramAI was designed specifically around the corporate entity hierarchy:
`
TENANT (Holding Group / Corporate Headquarters)
└── Master Organization (Group HQ Governance & Global Policy)
├── Operating Subsidiary A (Automotive Group)
├── Operating Subsidiary B (Healthcare Diagnostics)
└── Operating Subsidiary C (Consumer Financial Products)
`
1. Cryptographic Company Boundaries
Every child company exists within a hermetically sealed operating boundary. Documents, conversations, customer profiles, and team permissions are strictly locked to that specific subsidiary. A customer chatting with Subsidiary A can never access or trigger data from Subsidiary B.
2. Group Headquarters Control Plane
While subsidiaries operate in complete data isolation, group executive leaders maintain a unified Master Overview:
- Real-time performance metrics across all operating subsidiaries.
- Global policy enforcement (such as banned terms, regulatory disclaimers, and data protection rules).
- Consolidated billing and centralized cost allocation per company.
Executive Takeaway
Holding companies no longer need to choose between data security and operational efficiency. With BhavitramAI, multi-entity groups run autonomous, isolated AI agents for every subsidiary under one sovereign corporate umbrella.
Build Enterprise AI with Zero Data Traversal
Connect your databases, storage accounts, and WhatsApp numbers in minutes with built-in AST safety and preflight diagnostics.
Start Free Trial →